February 9, 2023
CJIS compliance for agencies and the vendors that serve them
Strike Graph maps the FBI’s CJIS Security Policy to NIST 800-53 controls, so you can protect criminal justice information and show your state CJIS Systems Agency the evidence.
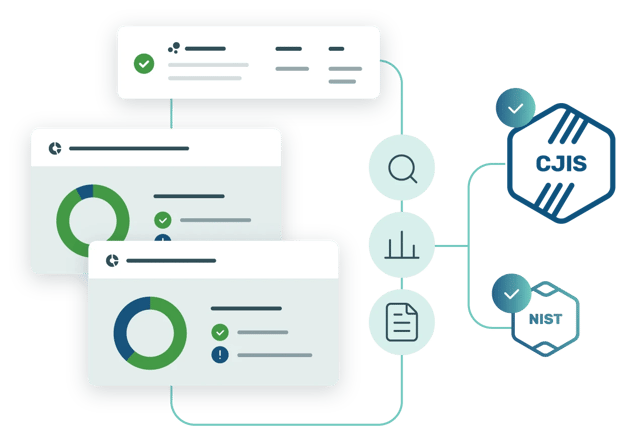
CJIS Security Policy v6.1 is built on NIST 800-53

Shaky ground
Version 6.1 organizes CJIS requirements around NIST 800-53 Rev. 5 control families. Track them in spreadsheets and every requirement becomes a one-off to document and evidence.

A strong foundation
Using Strike Graph to map your controls to NIST 800-53 covers CJIS and sets the foundation for FedRAMP and StateRAMP compliance as well.
What is CJIS?
The FBI’s Criminal Justice Information Services (CJIS) Division publishes the CJIS Security Policy, the minimum security requirements for any organization that accesses, stores, or transmits criminal justice information (CJI). It applies to law enforcement and other government agencies, and to the private contractors and cloud providers that handle CJI for them. There is no CJIS certification. Compliance is verified through audits by state CJIS Systems Agencies and by the agencies that contract with vendors.

Set yourself up for CJIS success
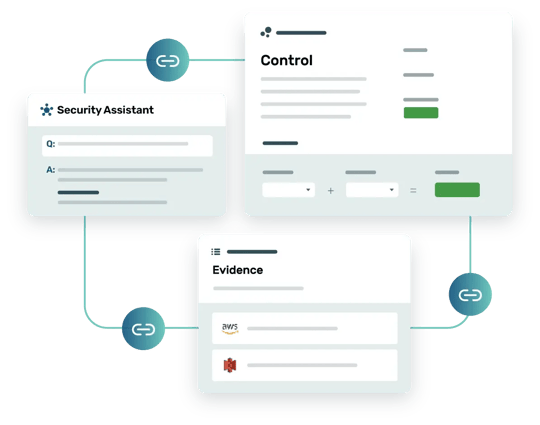
Accelerate compliance with AI
Strike Graph’s automated evidence collection, AI security assistant, and notifications make your CJIS process faster and easier.
Eliminate audit uncertainty
See where you stand before your CJIS audit does, with Strike Graph’s predictive audit capabilities.
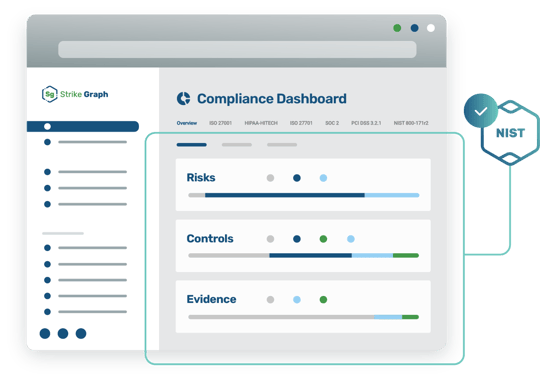
Produce what the auditor asks for
Generate a system security plan from your mapped controls. Monitor evidence continuously. Run internal audits with Verify AI. Export your CJIS-to-NIST 800-53 evidence for your CJIS Systems Agency.
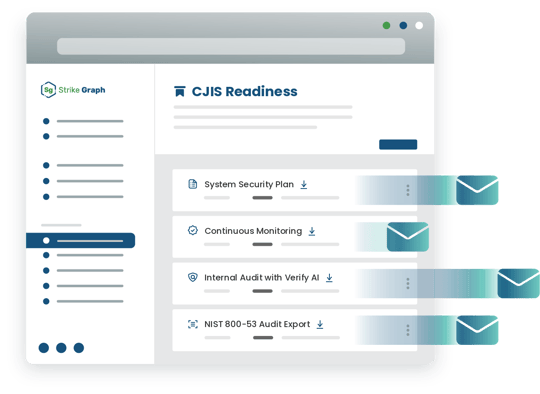
Packed with useful features

In-house penetration testing

Cross-framework support

55+ policy templates

Easy integrations
Here’s how it works.
Strike Graph keeps the CJIS Security Policy and NIST 800-53 compliance process simple.
Step 1
Identify your security gaps
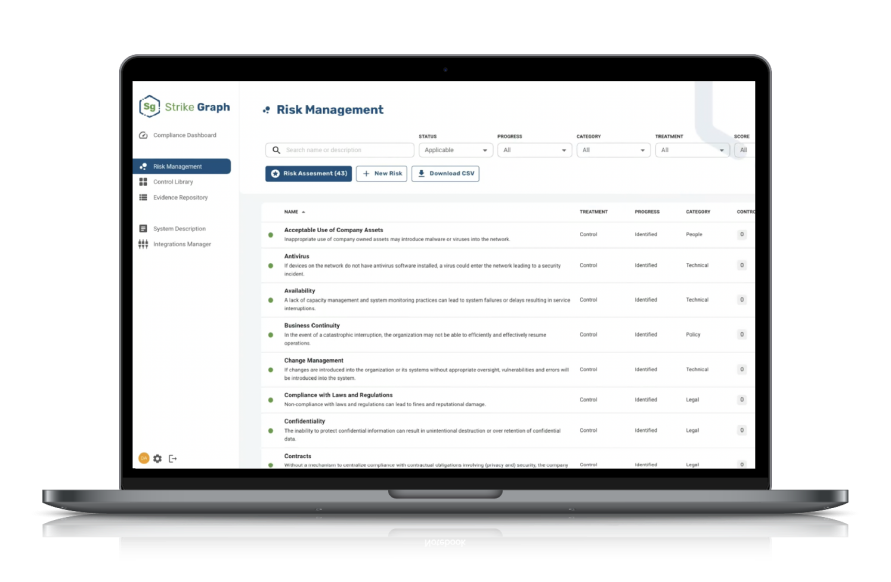
Strike Graph’s risk assessment and rating tools show where your environment falls short of CJIS requirements.
Step 2
Implement pre-mapped NIST and CJIS controls
Strike Graph’s library maps CJIS Security Policy requirements to NIST 800-53 controls. Choose from the library or customize controls to fit your exact needs.
Step 3
Prepare for your audit
Keep your evidence in one place, ready for when your state CJIS Systems Agency or contracting agency reviews your controls.

See what our customers think of Strike Graph.
Streamlining the compliance process
The pre-existing libraries to choose from are beneficial, as well as the ability to add our unique controls is highly efficient and user-friendly. … Strike Graph is an intuitive easy to use tool for efficiently working through the compliance process. Read more on G2.com
User in computer software
Strike Graph is your partner in compliance…
Strike Graph is your one-stop shop to get your security audits going and completed in half the time. There are file repositories for security audits, automated security questionnaires. evidence repository, and great support from the customer success team. Whether you need evidence of HIPAA, SOC2, or ISO, you're in the right place. Read more on G2.com
Administrator, information technology and services
Compliance powers confidence
I am pleased with the Strike Graph team helping us navigate our compliance ocean. I have been surprised how quickly we can make sense of the good policies and procedures we already have functioning internally with the frameworks we need to provide an attestation around. Read more on G2.com
Executive Sponsor in Computer Software
Strike Graph is trusted by hundreds of companies for security and compliance.




Dig into the details.
Want to know more about the CJIS Security Policy and how it connects to NIST 800-53? Wondering whether it applies to your agency or your company? Read on for answers.
What is CJIS?
CJIS is the FBI’s Criminal Justice Information Services Division. Its CJIS Security Policy sets the minimum security requirements for protecting criminal justice information (CJI), such as fingerprints and criminal history records, wherever it is accessed, stored, or transmitted.
Who has to comply with the CJIS Security Policy?
Criminal justice and other government agencies that access CJI, and the private contractors and cloud service providers that process CJI on their behalf. Each agency is responsible for its own compliance, including its use of cloud services.
Do vendors have to comply? What is the CJIS Security Addendum?
Yes. Private contractors that process CJI sign the CJIS Security Addendum (Appendix H of the policy), a uniform agreement that commits the contractor to a security program consistent with federal and state law and limits use of CJI to the purposes the agency provided it for. State CJIS Systems Agencies may require their own agreements as well, and the policy sets personnel screening requirements for contractor staff with access to CJI.
What changed in CJIS Security Policy v6.1?
Version 6.x is organized around NIST 800-53 Rev. 5 control families instead of the 13 policy areas used in v5.x, and it renames several roles. For example, Contracting Agency replaces CGA, and IA Official replaces Compact Officer. It also puts more weight on continuous risk management and on evidence that controls are reviewed over time.
When do I have to meet version 6.1?
Audit timing is set by your state CJIS Systems Agency, and the version in force for your audit can differ from the latest published policy. Confirm the version and the dates with your CSA.
Is there a CJIS certification?
No. CJIS compliance is verified through audits by state CJIS Systems Agencies and the FBI, and by agencies auditing their contractors, so there is no CJIS certificate to earn. Strike Graph helps you prepare the controls and evidence those audits ask for.
How does Strike Graph help with CJIS?
Strike Graph maps CJIS Security Policy requirements to NIST 800-53 controls, collects evidence from your systems, tracks gaps, and keeps your documentation audit-ready. Tag vendors that touch CJI, store each exchange agreement as an evidence item that gets tested, and get reminded when an agreement is out of date. The same controls and evidence support FedRAMP, StateRAMP, and other frameworks.
Can’t find the answer you’re looking for? Contact our team!
Related resources
Check out more helpful guides from the Strike Graph team!
June 28, 2023

March 21, 2023
December 14, 2022
Related NIST 800-53 resources
Check out more helpful guides from the Strike Graph team!
November 17, 2022
Want to know more?
Schedule a demo and one of our compliance experts will walk you through how Strike Graph maps to CJIS requirements for agencies and vendors.