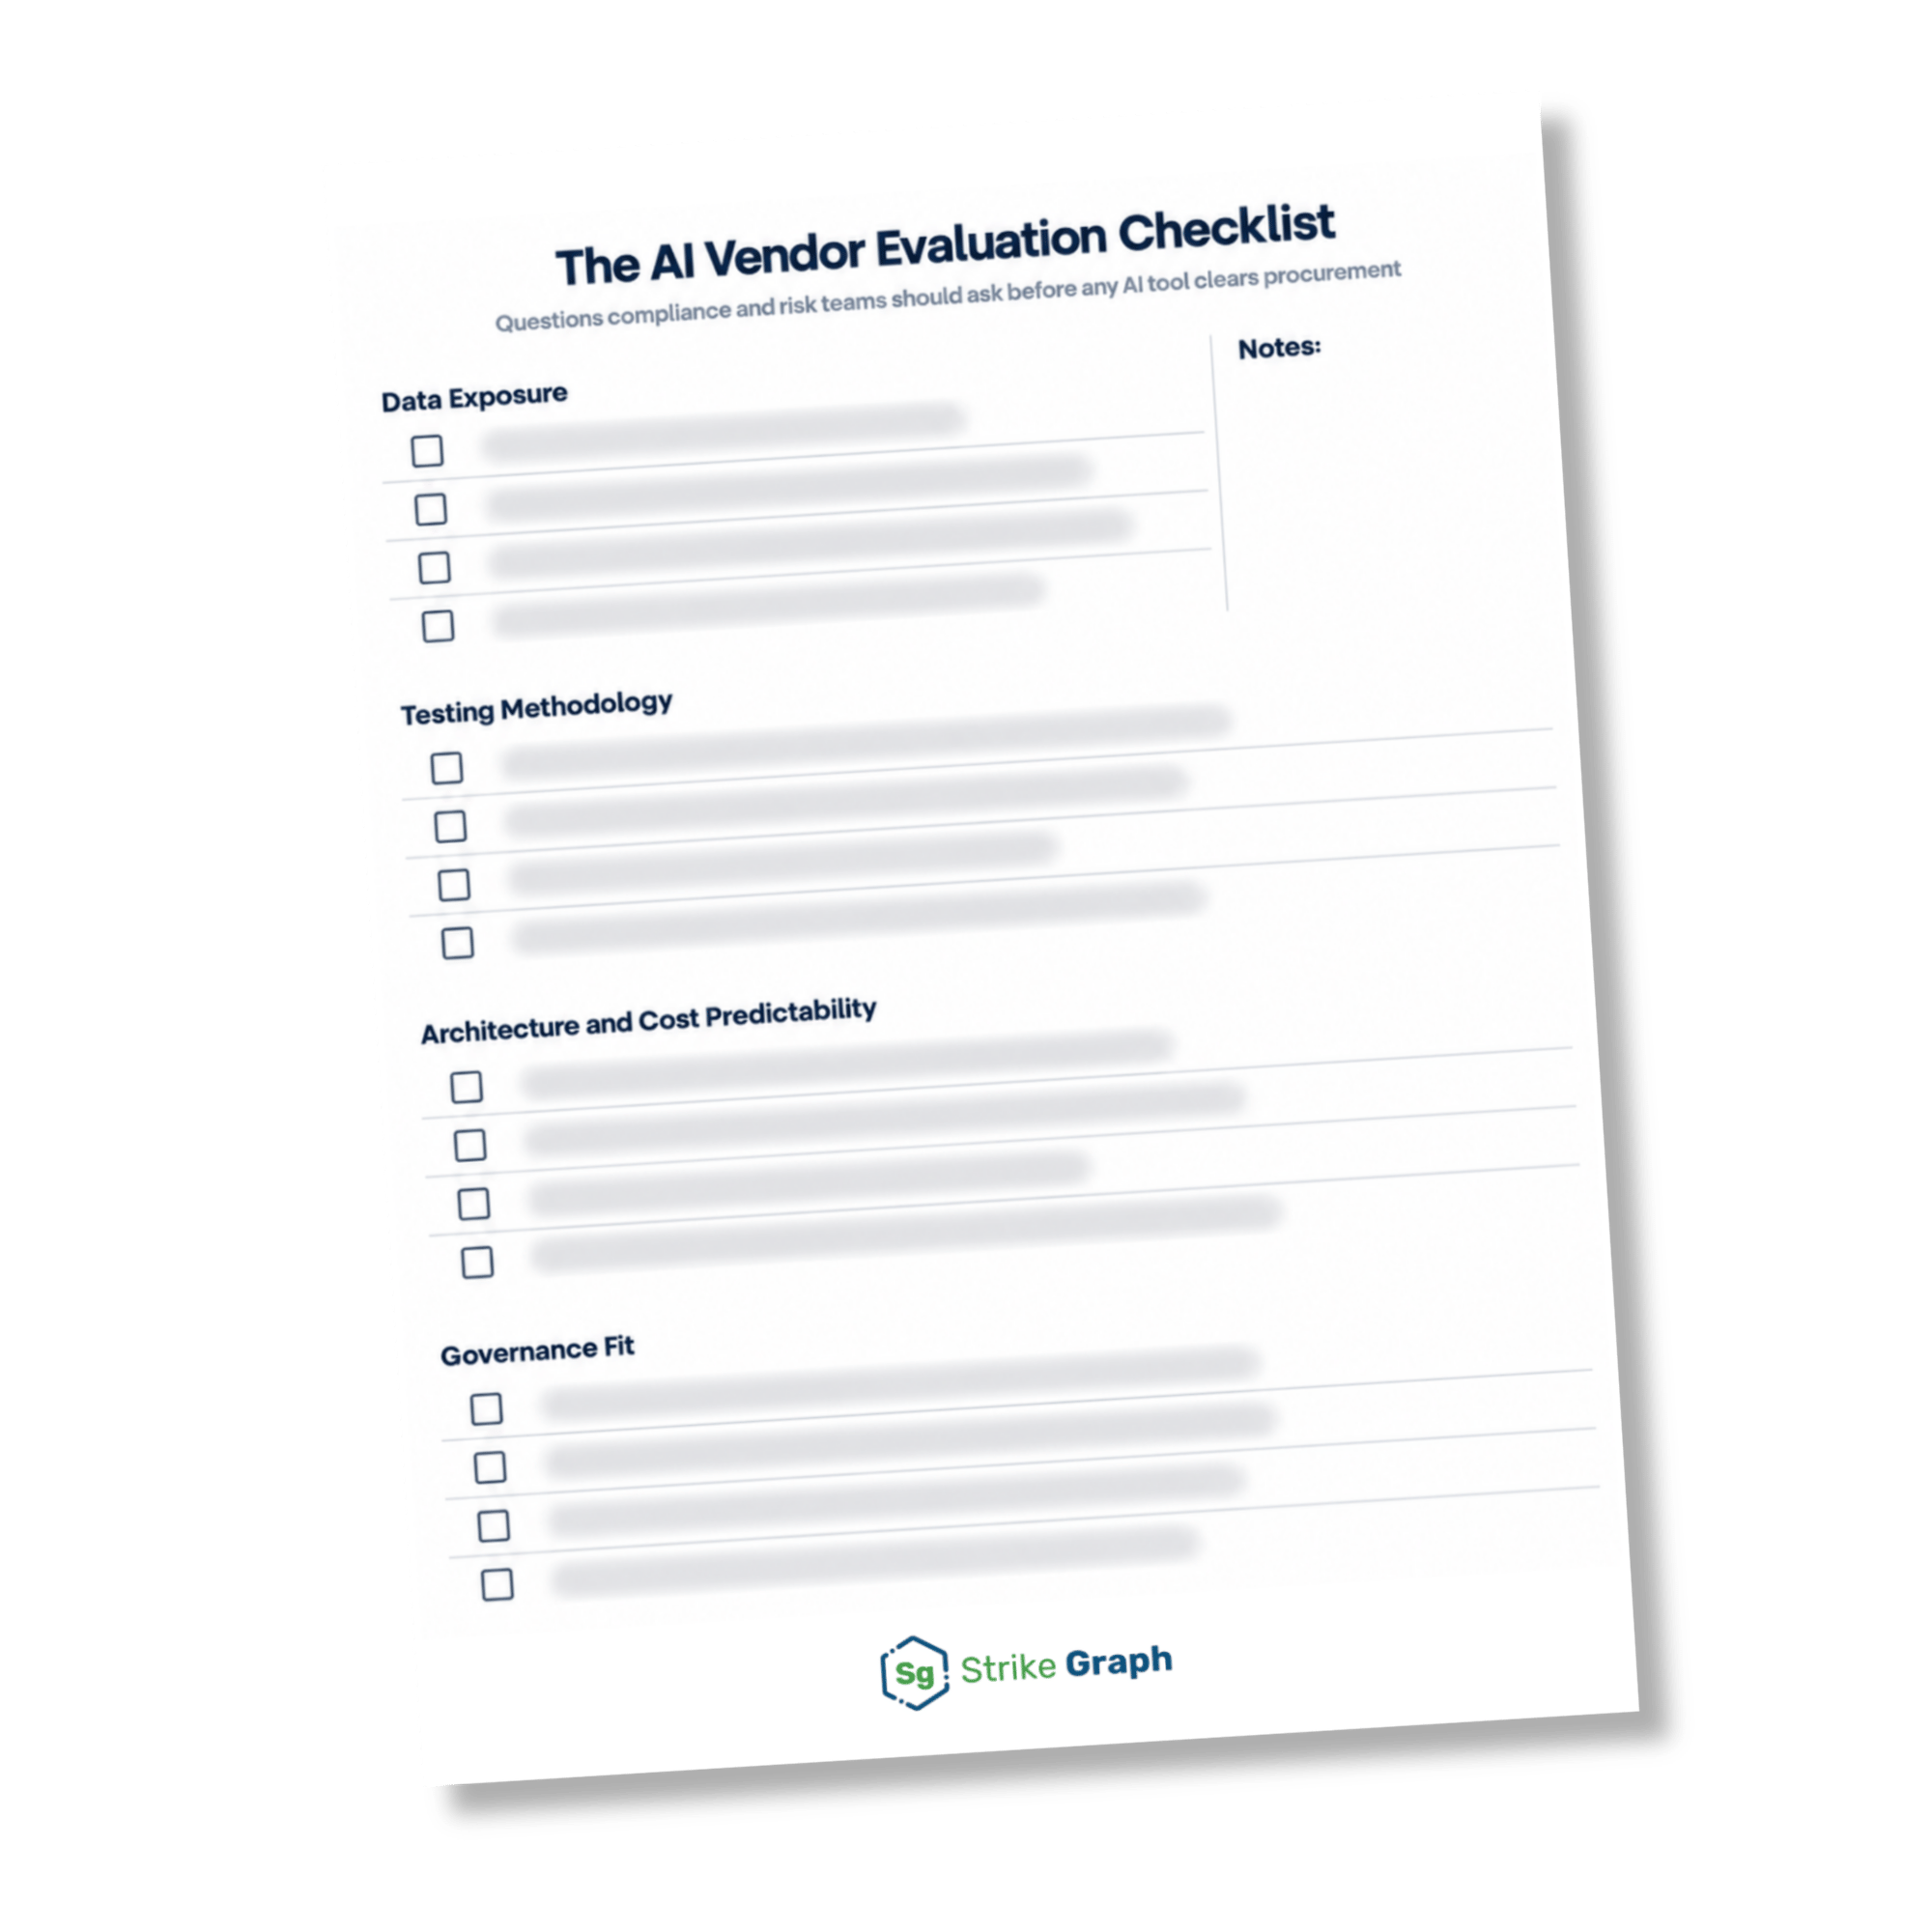
The AI Vendor Evaluation Checklist
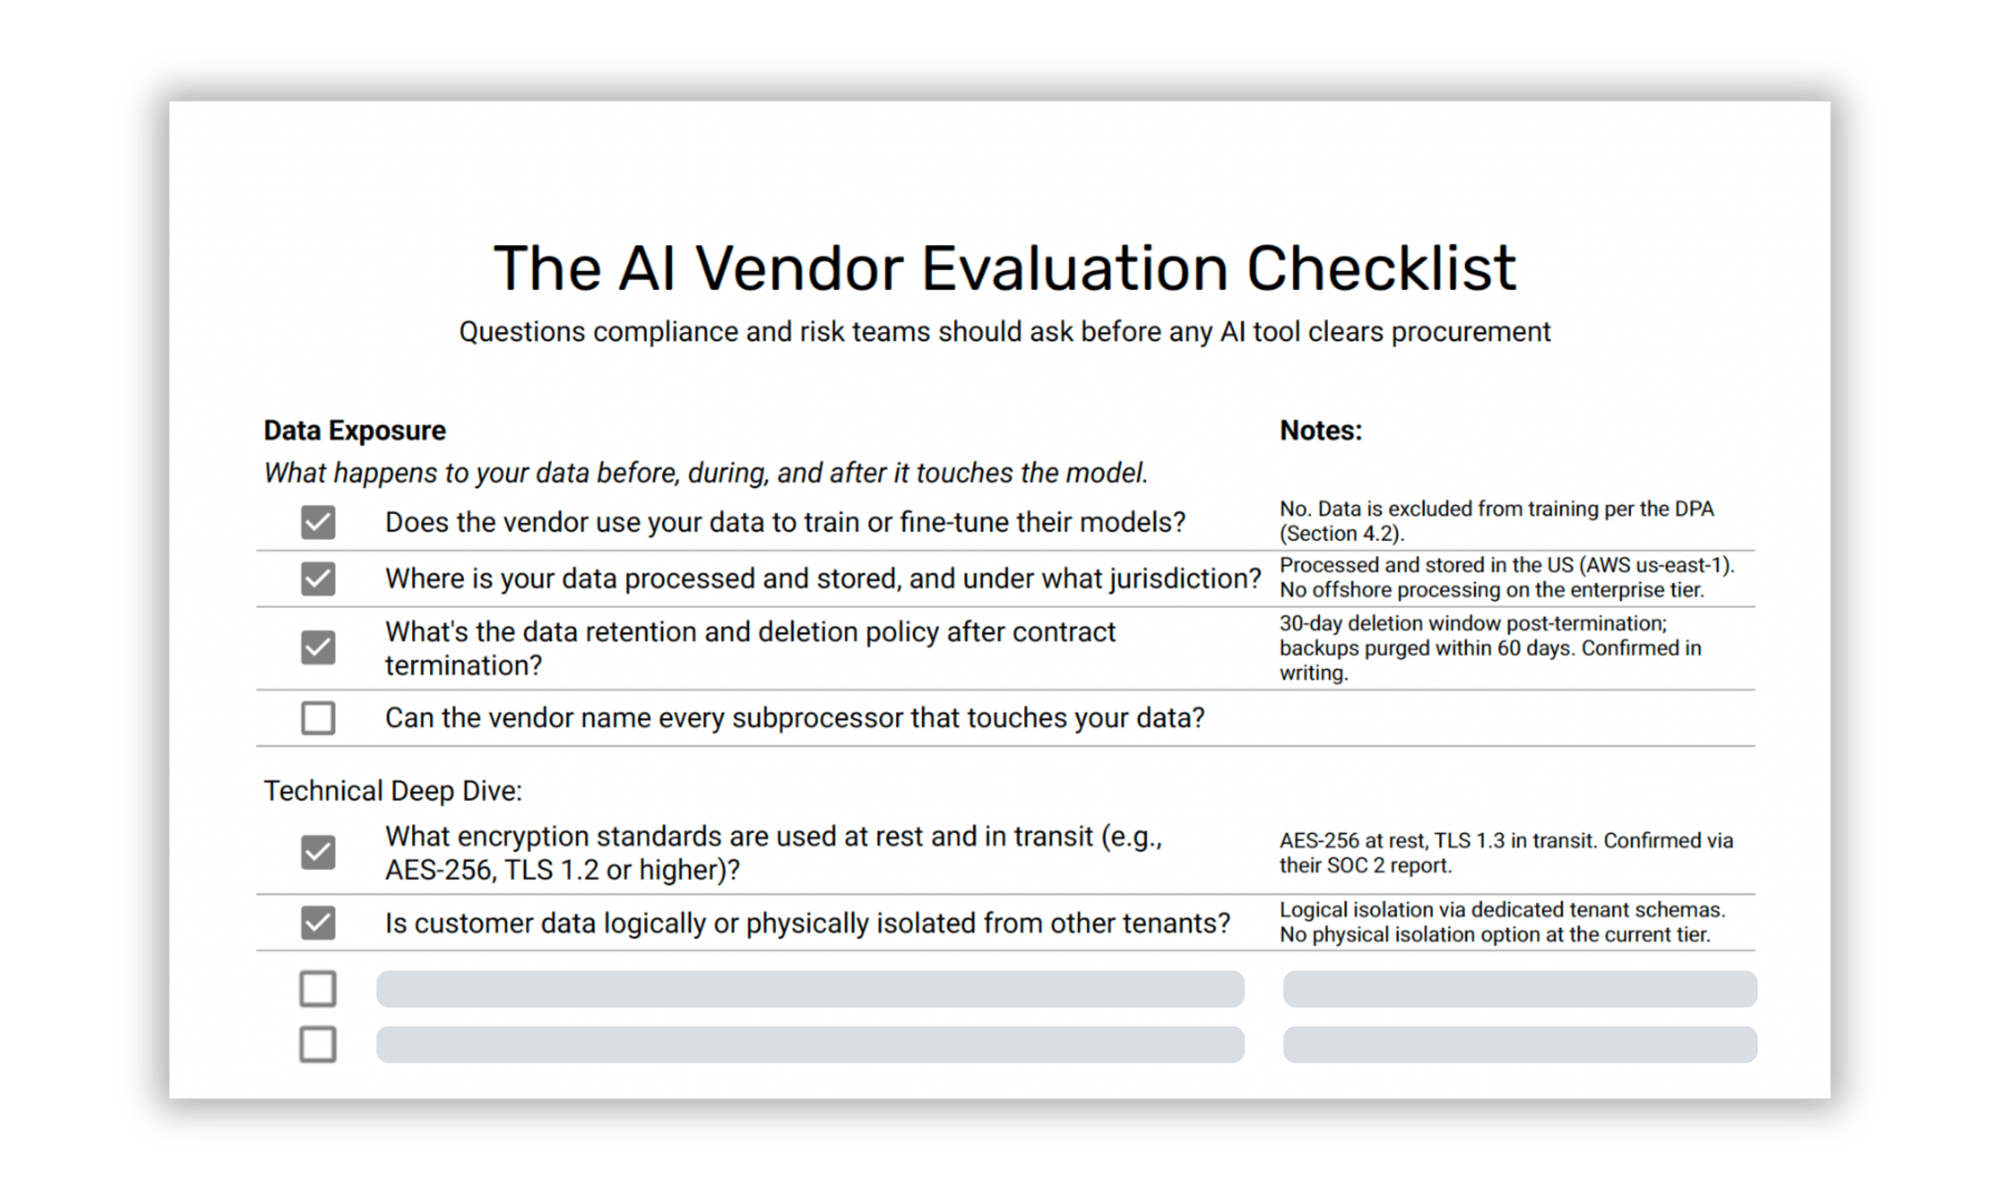
Most vendor security questionnaires weren't built for AI. This checklist gives compliance, risk, and GRC teams 35 specific questions to bring into any AI vendor review, covering data exposure, testing methodology, architecture, and governance fit, plus a technical deep dive for security and engineering reviewers. Download it today to bring structure to your next AI vendor review.
Get the checklist
What's inside the checklist
Built around four categories drawn from how AI tools actually create risk, not a repurposed version of a traditional vendor security questionnaire.

Where your data goes, and who else touches it
Understand what happens to your data before, during, and after it reaches the model, including retention, jurisdiction, and every subprocessor in the chain.

Whether the vendor can prove its testing, not just claim it
The specific questions that separate a vendor who tests rigorously from one who says "we test for accuracy" with nothing to back it up.

Why architecture determines both risk and runaway cost
How a vendor's underlying model architecture affects data isolation, output consistency, and whether token spend stays predictable at scale.
Your AI vendor's certificate proves less than you think
An ISO 42001 certificate and a clean SOC 2 report confirm your vendor followed a process. Neither proves the AI itself works, or that anyone tested whether it does. Read the research behind all four major AI governance frameworks, what they actually cover, where they stop, and what that means for your next AI vendor review.
How Strike Graph helps you act on what the checklist surfaces

Continuous vendor risk tracking
Move past one-time questionnaires. Track AI vendor risk posture over time as certifications, architecture, and data practices change.

Centralized evidence for every AI vendor
Keep testing documentation, certification scope, and data practices in one place instead of scattered across email threads and spreadsheets.

Governance fit, not just security fit
See whether a vendor's certification actually covers the AI system you're evaluating, not just the infrastructure around it.

Built for the questions this checklist raises
Evaluation criteria that mirror the checklist's categories, so what you ask up front is what you track going forward.

Audit-ready documentation
Turn vendor evaluation answers into evidence you can produce for your own compliance audits, without rebuilding the record from scratch.

One system for every AI vendor you bring in
As AI tools multiply across your organization, keep every vendor's evaluation and ongoing risk status under one system instead of one-off reviews.
Trusted by hundreds of fast-growing companies


